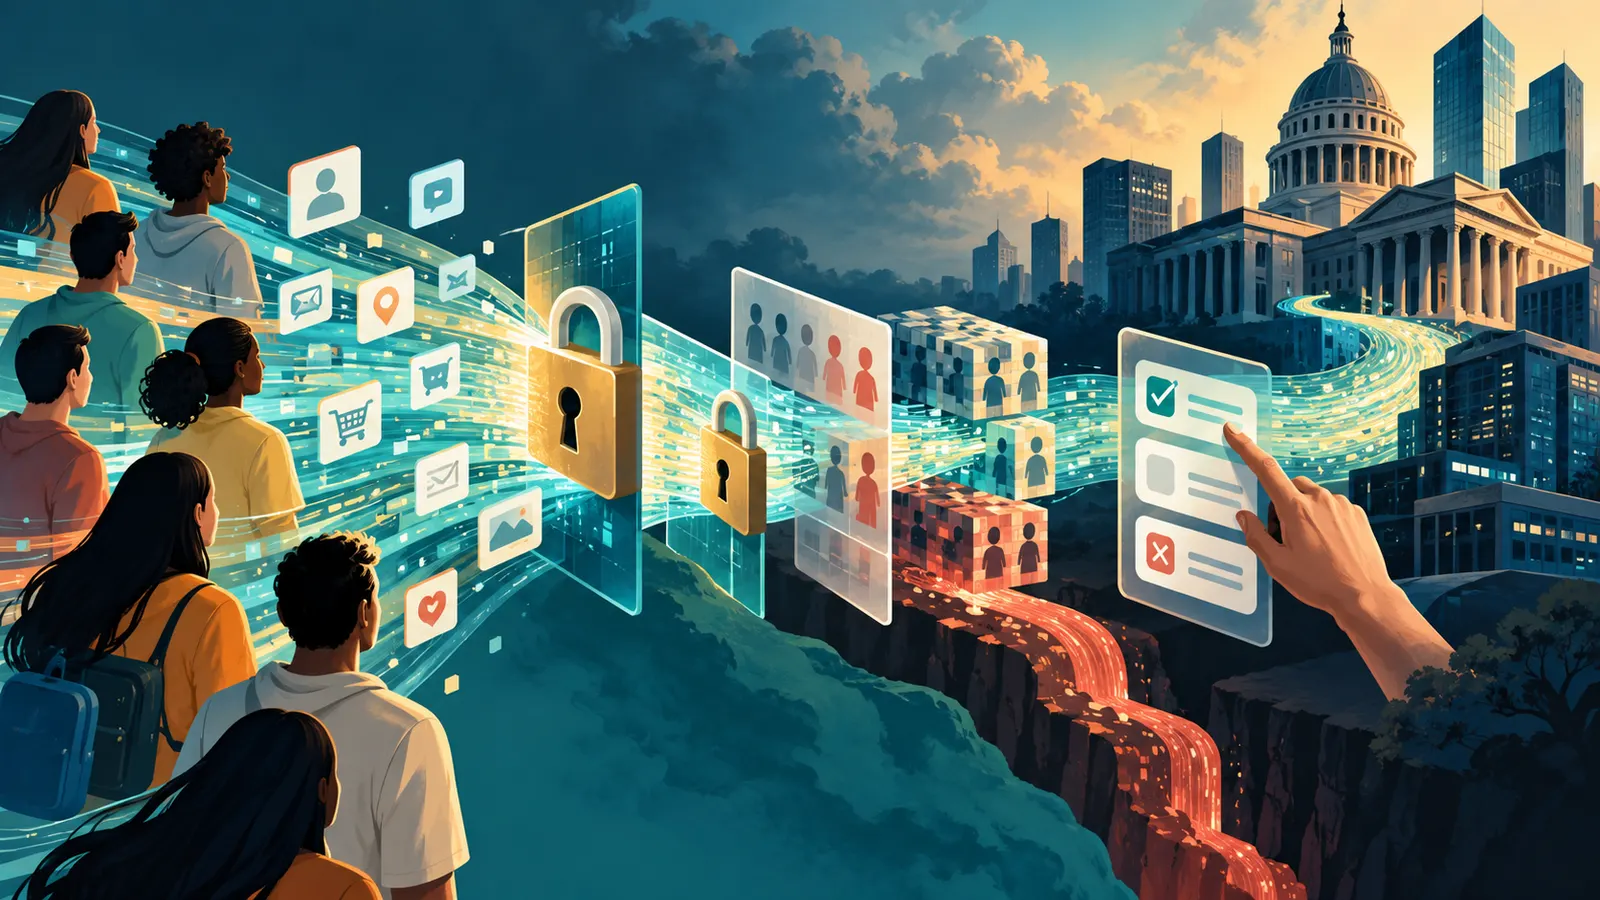
People often describe personal data as a price paid for a free service. The exchange appears voluntary: use an application without handing over money, and provide information about activity in return. But the analogy between data and a simple payment is imperfect. A payment usually ends at a known amount. Information can be copied, combined with other information, interpreted in ways that change, and used long after the original encounter. What was apparently surrendered at one moment may acquire a different value later.
An individual detail may seem harmless. A person buys a particular product, visits a website, or travels a familiar route. In combination, such details can reveal routines, associations, and preferences that were never explicitly disclosed. A name is not always necessary to make an account informative. A sufficiently distinctive pattern of behaviour may identify someone or allow a company to make consequential guesses about them. Privacy is therefore not simply a matter of hiding a few sensitive facts.
This does not imply that collecting data is always wrong. Information can help a service remember a user's settings, detect suspicious transactions, improve an accessibility feature, or understand where a public service fails. The benefits are real. The question is which information is needed, for how long, under whose control, and with what consequences if it escapes or is repurposed. The promise of future usefulness cannot by itself justify indefinite collection.
Consent is often presented as the answer. In principle, a user reads a notice and chooses whether to proceed. In practice, the notice may be long, the alternatives limited, and the consequences difficult to predict. A person cannot negotiate each clause of dozens of services used for education, work, transport, and communication. Clicking 'agree' records an action, but it does not prove that the resulting relationship is fair. Good governance needs limits and responsibilities that survive an inattentive click.
There is a collective dimension to data as well. One person's decision to share a photograph may reveal information about friends. A genetic record can contain clues about relatives. A map made from many individuals' movements can describe a community even if some residents never joined the service. The effects of disclosure do not always stop at the boundary of the person who consented. This complicates the image of privacy as a purely individual possession to trade away.
Advocates of extensive data collection point to the value of improved prediction. If a system knows more, perhaps it can recommend better routes, detect fraud more effectively, or tailor learning to a student's difficulties. Sometimes it can. Yet more data can introduce noise, store outdated assumptions, and encourage an organisation to solve a problem through surveillance rather than through simpler design. The relevant question is not how much information can be gathered, but how much is justified by a specific purpose.
Data can also shape the opportunities offered to a person. A prediction about spending, reliability, or likely interest might determine which advertisement, price, or invitation appears on a screen. The user may never know which alternatives were withheld. In such cases, privacy is connected to fairness and autonomy: a record about past behaviour influences the choices available in the present. An inaccurate inference can be hard to contest if the system that made it remains invisible.
Deletion is often more complicated than removing a visible account. Information may have been backed up, summarised, or incorporated into other systems. Even when a service follows clear rules, the technical life of data may differ from the ordinary user's expectation that pressing delete makes something disappear everywhere. Transparent design should explain what can actually be removed and what consequences remain. Vague reassurances are poor substitutes for understandable controls.
There are ways to design a less demanding exchange. A service can collect fewer fields, retain them for shorter periods, process some information on a user's device, or make important features available without creating a detailed profile. Each choice involves costs and technical constraints. But they demonstrate that the amount of data collected is a design decision rather than a law of nature. Convenience can be produced in more than one way.
The phrase 'I have nothing to hide' misses much of the point. People need space to experiment, change their minds, and communicate differently across relationships without every action being assembled into a permanent account. Privacy is not a request to escape all accountability. It is a condition under which ordinary freedom can be exercised without constant observation. A free service may offer value, but the terms of its information exchange deserve the same scrutiny as any price we are asked to pay.
Security and privacy should also be distinguished. A company may protect its databases expertly against unauthorised access while still collecting much more information than its service requires. Conversely, a service may promise modest collection but fail to protect the records it does hold. Both questions matter: who is permitted to obtain information, and how safely is it stored? Treating secure storage as a complete answer overlooks the possibility that an organisation's authorised use is itself too broad.
The harms of collection can be difficult to demonstrate in advance. A harmless-looking archive may become sensitive when a new technique allows information to be combined across sources. A person may not know that an inference was made, much less which choice it influenced. This uncertainty argues for restraint in collecting data, especially when the expected benefit is vague. It does not follow that every possible future misuse is inevitable; it follows that the cost of preserving an unnecessary record should be counted alongside the promised benefit.
Clearer options could improve the relationship between users and services. A person might allow data needed to operate a feature while declining unrelated profiling. Explanations could describe what a choice actually changes instead of relying on broad labels such as 'personalisation'. Some limits should be built into the design rather than shifted onto a user who has little time to study technical settings. A meaningful choice needs a realistic alternative as well as a button to press.